What the ASOS cyber incident reveals about third-party risk
Subscribe to our free newsletter today to keep up to date with the latest retail news.
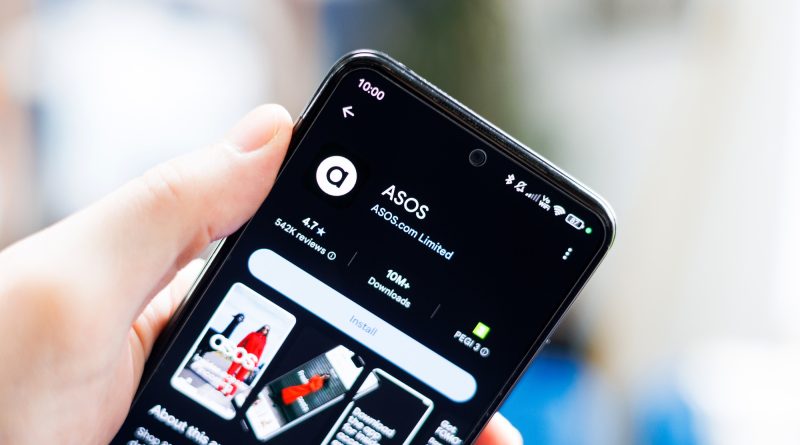
ASOS is investigating unauthorized activity involving third-party platforms after customers received an unauthorized push notification, putting supplier cyber security under renewed scrutiny.
The online fashion retailer said the incident occurred on Oct. 6 through platforms it uses to communicate with customers. It restricted access to its notification systems and began working with internal and external specialists, as well as relevant authorities.
ASOS said basic personal information, including names and contact details, may have been accessed. It does not believe payment card information or account passwords were affected. Its website and app remained operational.
The incident appears limited compared with some recent retail cyber attacks. Even so, it raises a wider issue for businesses that depend on large networks of software, cloud and service providers.
A company may control its own systems, but parts of its customer experience can still sit in the hands of outside providers.
For retailers, manufacturers, logistics companies and other connected businesses, that creates a wider field of cyber risk.
Businesses rely on suppliers more than they assess cyber risk
Third-party technology is now embedded across everyday business operations.
Retailers may use outside providers for customer communications, payments, cloud storage, inventory management and marketing. Manufacturers depend on software vendors, equipment providers and connected suppliers. Logistics companies rely on transport platforms, warehouse systems and digital networks that link several businesses.
Each connection can add another point of exposure.
UK government data suggests many businesses still do relatively little to assess that risk.
The Cyber Security Breaches Survey 2025/2026 found that only 15% of UK businesses formally reviewed cyber security risks from their immediate suppliers. Just 6% assessed risks across their wider supply chain.
Larger companies performed better, but gaps remained. Around 48% of large businesses reviewed risks from immediate suppliers, while only 24% examined their wider supply chain.
This matters because companies increasingly share data and system access across organizational boundaries.
One supplier might store personal information. Another may have access to internal software. A communications provider may be able to send messages directly to customers.
The ASOS incident shows why those relationships need to form part of a company’s wider risk planning.
ASOS said the activity involved third-party platforms used for customer communications. The company restricted access after an unauthorized customer notification was sent.
For business leaders, the lesson is not that outside technology should be avoided. Many modern operations depend on it.
The question is whether supplier access, permissions and incident plans receive the same level of attention as systems operated inside the business.
A cyber incident does not have to stop operations to cause damage
The ASOS website and app continued operating normally after the incident. There was no reported disruption to wider operations at the time of the company’s regulatory statement.
That distinction matters.
Cyber resilience is often measured by downtime. Boards may ask how quickly factories, websites, warehouses or payment systems could recover after an attack.
Operational continuity is only part of the risk.
The ASOS incident reached customers through a communication channel they associate with the company. The unauthorized notification claimed that the retailer had been compromised and included an external Telegram link. ASOS later told customers to ignore the message and not interact with the link.
That creates a different form of exposure.
If attackers gain access to a trusted communication system, they may also gain access to the company’s relationship with its customers. Core operations can remain online while the business still faces questions about data protection, fraud, reputation and future phishing attempts.
Recent incidents elsewhere in UK retail show how quickly cyber problems can also become financial problems.
Co-op said a 2025 cyber attack had an estimated £285 million impact on sales and reduced its bottom line by about £86 million.
The ASOS incident should not be treated as equivalent. There is no evidence so far of disruption on that scale.
ASOS said on Oct. 6 that it was too early to quantify any potential effect on trading. It also confirmed that it holds cyber security and business continuity insurance.
The wider point is that cyber incidents now sit firmly within commercial risk.
Supplier security is becoming a board-level resilience issue
Businesses cannot remove every third-party risk, but they can improve their understanding of where those risks sit.
That starts with visibility.
Companies need to know which suppliers hold sensitive information, which have access to internal systems and which can communicate directly with customers.
Access rights also need regular review. A supplier should have only the permissions required to provide its service. Businesses should also know how quickly that access can be suspended if something goes wrong.
Incident planning should extend beyond systems owned by the company. A response plan that covers an internal breach but not the compromise of a major software or communications provider leaves an obvious gap.
Supplier contracts, cyber insurance and recovery plans also need to reflect the operational importance of third-party platforms.
The UK government’s latest figures suggest this work is still far from routine. Only 11% of businesses said they required suppliers to hold cyber security standards or accreditations.
That figure points to a wider business problem.
Companies have spent years connecting systems, suppliers and service providers to improve speed and efficiency. Those connections now form part of their cyber exposure.
The ASOS incident offers a timely example. A company can keep its website running and its core operations moving while still facing a security problem that reaches customers through an outside platform.
For executives, cyber resilience now has to extend beyond the company’s own network. It also has to account for the businesses and technology providers connected to it.
Source:
The Independent